🔐Cloudflare Builds Post-Quantum Certificate Authority, Cuts Handshake Time 9% in Chrome Test
Your TLS handshakes are about to get lighter
TL;DR
Cloudflare is building a public certificate authority for Merkle Tree Certificates, a post-quantum alternative to classic chains. A Chrome experiment showed 9% faster median performance. Chrome's quantum-resistant Root Store inclusion is targeted for early 2027.
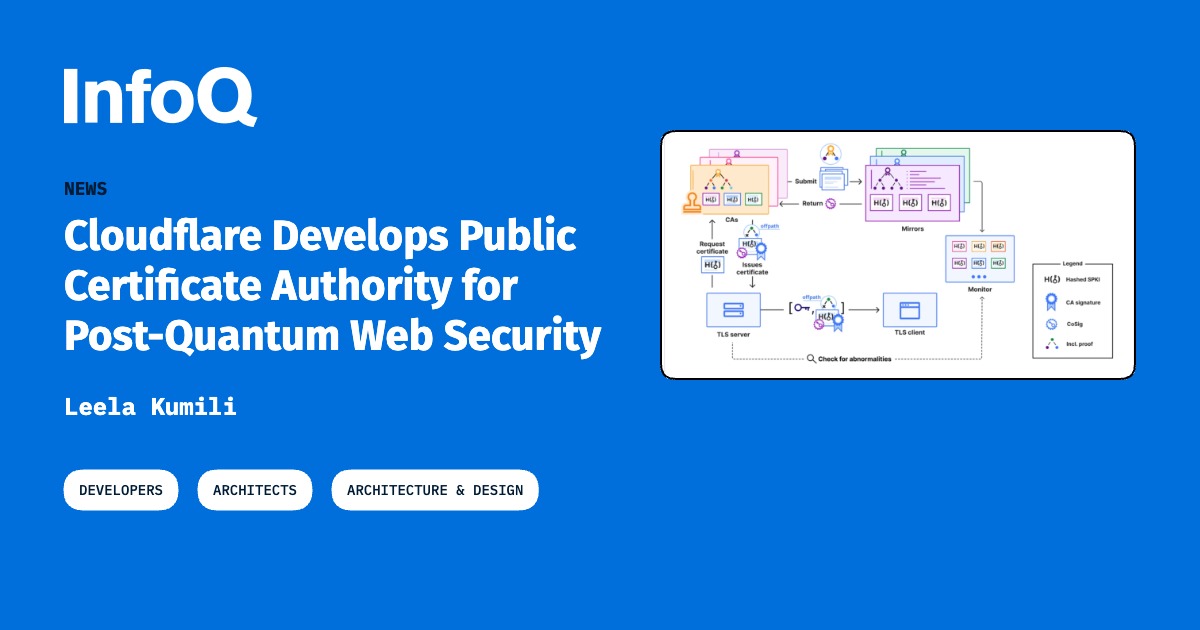
Cloudflare just built a public certificate authority for post-quantum web security, and the trick is getting rid of certificate chains entirely. Its Merkle Tree Certificates batch certificate data into an append-only tree, so clients verify with a compact inclusion proof instead of walking intermediates. Why you should care: post-quantum signatures are about 40 times larger than classical ones. That bloats every handshake. If you run TLS termination, this is the approach that could keep PQ migration from wrecking your bandwidth budget. Servers still have to keep a standalone MTC certificate as a fallback, so don't rip out your current setup yet. The numbers so far: a Chrome experiment showed a 9% faster median, but it used classical signatures, not PQ ones. The handshake now carries one public key, one signature, and an inclusion proof under 1 KB. Landmark relative certificates shave off even more data, and an independent mirroring cosigner keeps the tree honest. What to watch: Cloudflare still needs independent monitoring at production volume, a diverse set of CAs and cosigners, and browser support. Chrome inclusion is targeted for early 2027, and that's when this gets real.
Key Points
Post-quantum signatures can be roughly 40 times larger than classical signatures, which inflates bandwidth and storage for every TLS handshake on the wire today.
Keep reading — it's free
Enter your email to keep reading — plus the best of AI & tech, daily. Free, forever.
Already a member? Sign in
Comments
Be the first to comment