🔐Security Fix Stalled by AI Safeguards: One-Line Patch Waits Days for Exemption
Your one-line security fix might wait days for permission
TL;DR
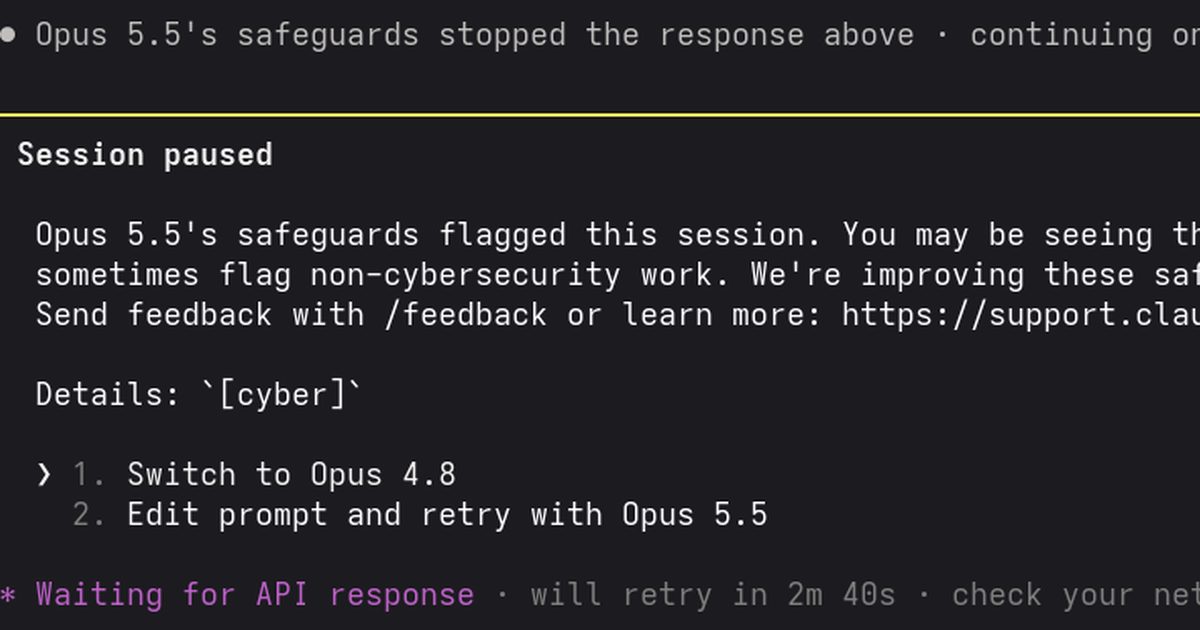
A simple one-line security fix was blocked by AI safeguards. Getting an exemption takes multiple business days, requires ID, forfeits data retention rights, and may be denied. Teams should plan for open-weights models hosted in the EU.
A security issue turned up in a project, and the fix was one line long. Then AI safeguards stopped it. The patch could not go in without an exemption, and the exemption process is slow. Expect multiple business days before anyone responds, and the approval may never come. If you maintain code that touches AI tooling, this is your problem too. Applying for an exemption also forfeits any data retention exemptions you hold, and it requires submitting identification such as a passport or ID card. Teams that rely on AI-assisted security review now have to weigh that overhead against how fast they need to ship a patch. The numbers are blunt: a one-line change, a multi-day wait, a non-trivial chance of rejection, and a permanent loss of retention exemptions. Meanwhile, public proof-of-concept snippets can be adapted for attacks on services, and criminals do not ask for approval before using unsafeguarded models. The fix that worked here came from EU-hosted open-weights models such as GLM 5.3, which helped both fix and verify the issue. Worth watching: whether labs loosen exemption paths for defenders before the next incident forces the question.
Key Points
A one-line security fix was blocked by AI safeguards, delaying a patch that could have shipped immediately without any tooling friction at all.
Keep reading — it's free
Enter your email to keep reading — plus the best of AI & tech, daily. Free, forever.
Already a member? Sign in
Comments
Be the first to comment