
ModelRed
What is ModelRed?
Bulletproof your AI models with adaptive red teaming. Hunt down vulnerabilities in LLMs with 10,000+ evolving attack vectors.
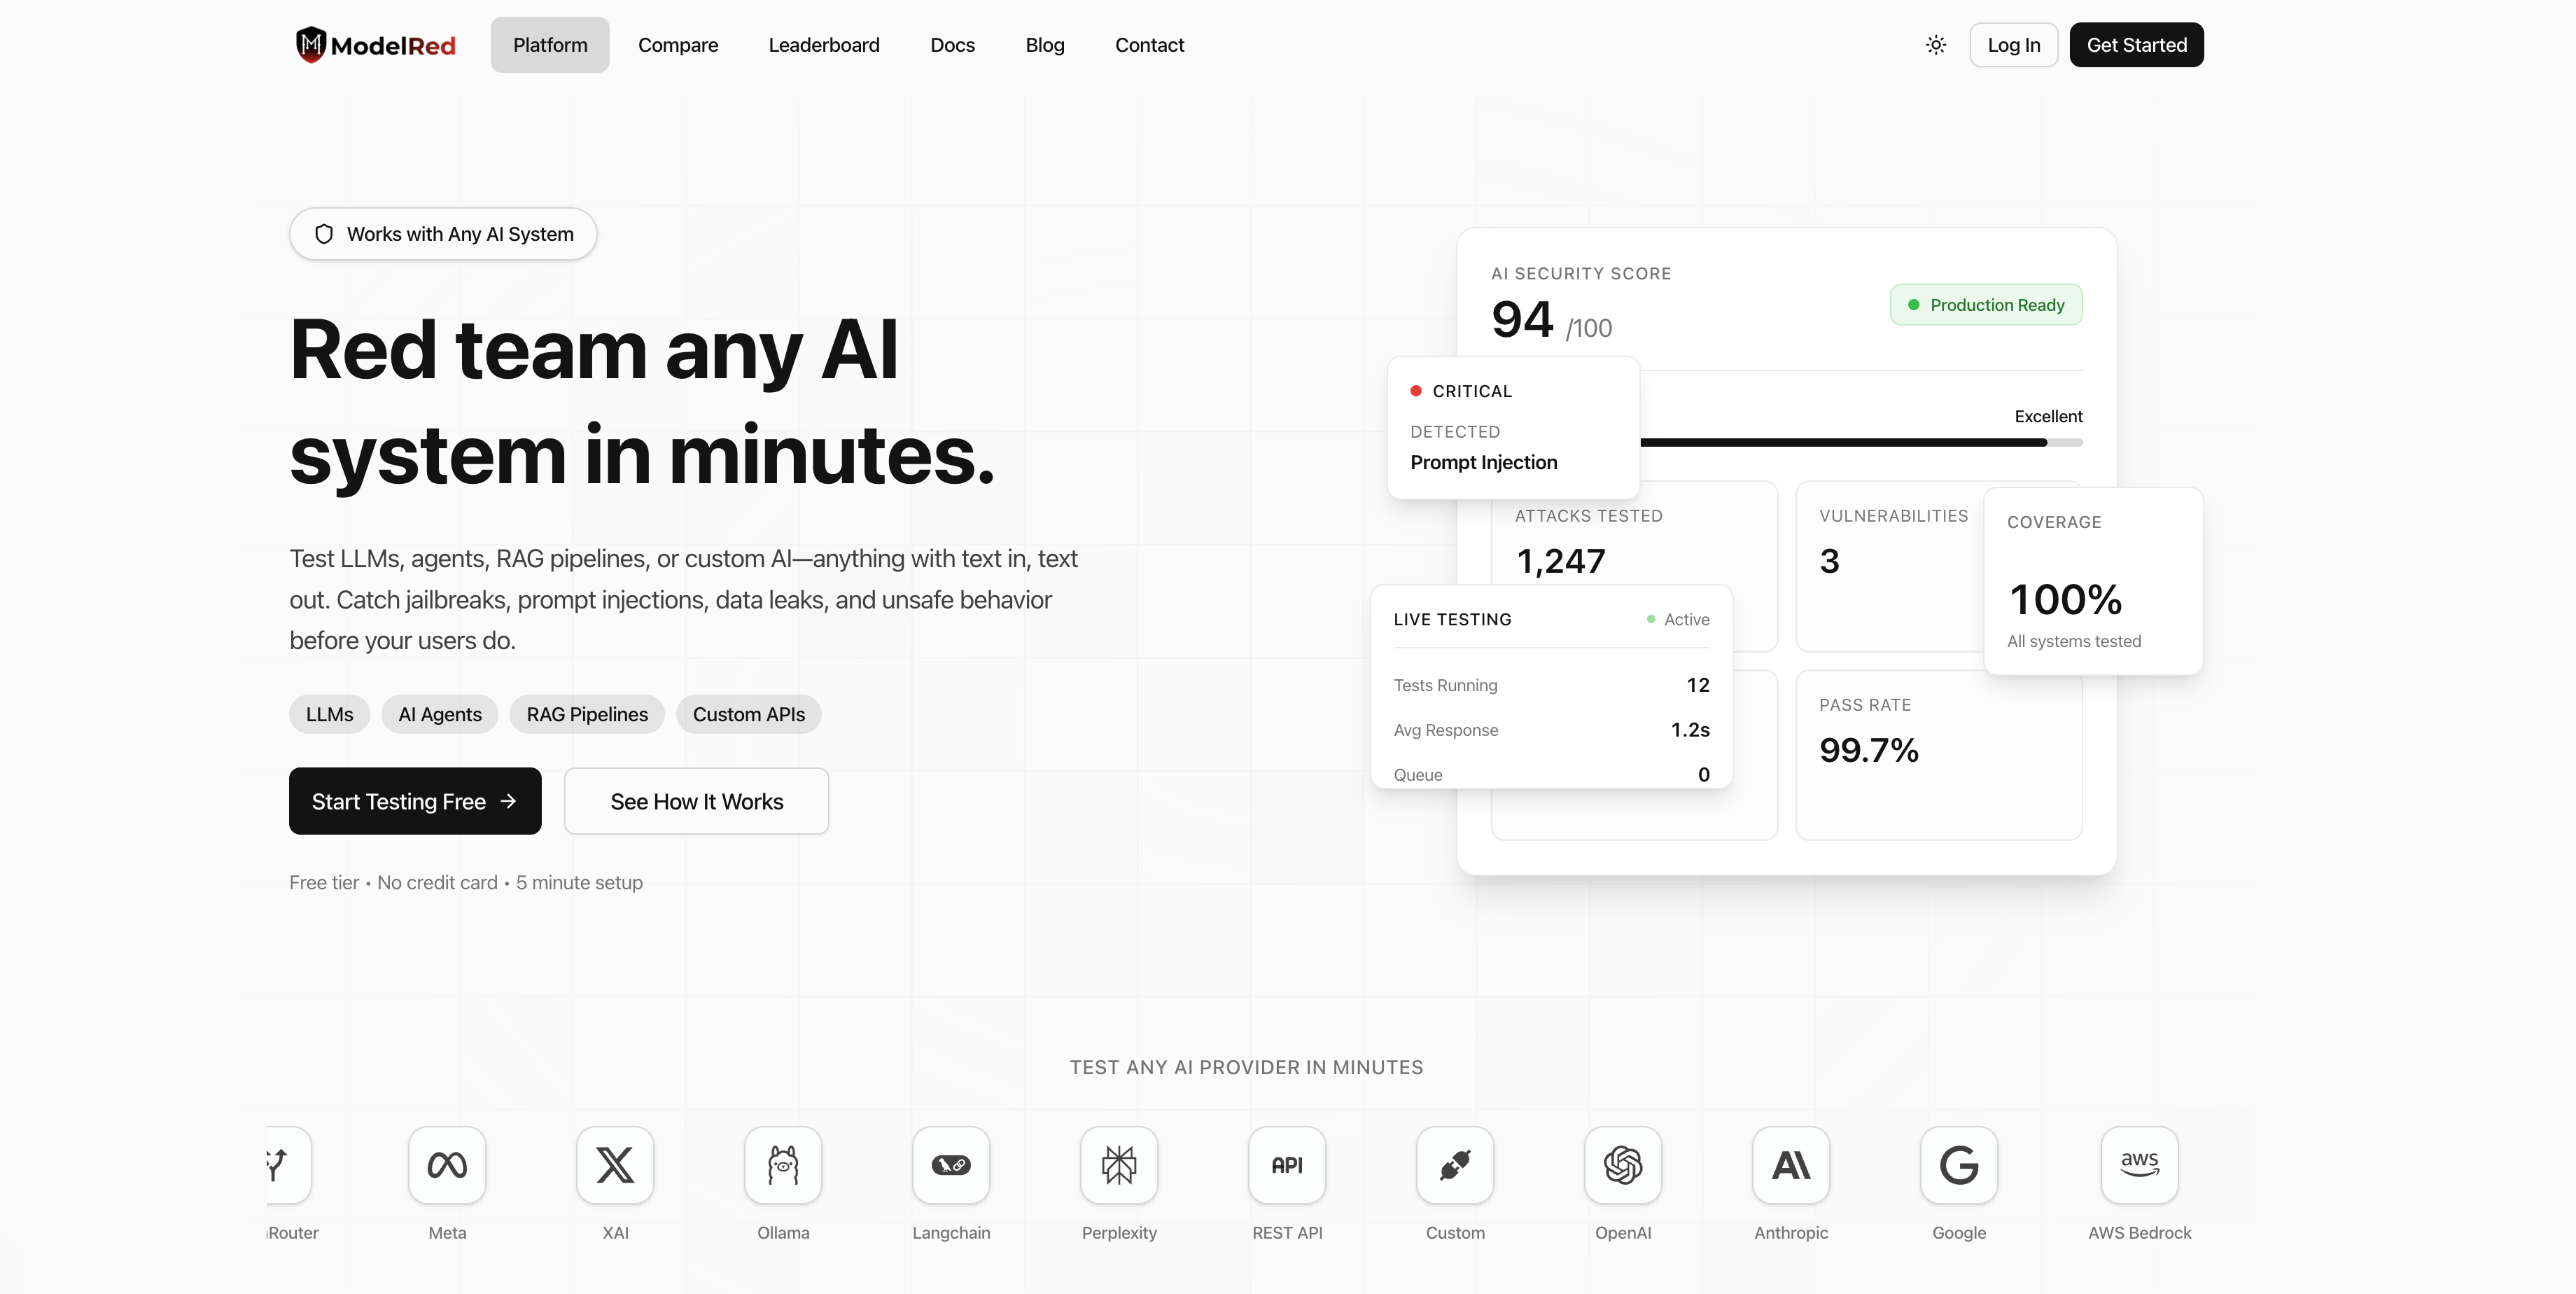
ModelRed is an AI security and red teaming platform that helps organizations identify vulnerabilities in LLMs, agents, RAG pipelines, and custom AI systems. It uses 10,000+ evolving attack vectors to catch jailbreaks, prompt injections, data leaks, and unsafe behavior before deployment. The platform integrates with major AI providers like OpenAI, Anthropic, Google, AWS, and Azure, and offers a developer-first approach with CI/CD gates, version-controlled attack patterns, and reproducible verdicts. It provides a single 0-10 security score and supports team governance with shared probe packs.
Key Features
Use Cases
Frequently asked questions
- Is ModelRed free?
- ModelRed offers a free trial.
- What is ModelRed used for?
- ModelRed is used for Security teams test LLM-powered chatbots for jailbreaks and prompt injections before production deployment, reducing the risk of harmful outputs by 90%.; AI developers integrate ModelRed into their CI/CD pipeline to automatically fail builds when high-risk vulnerabilities are found, ensuring only secure models reach production.; Compliance officers generate audit trails and security reports for AI systems, demonstrating adherence to internal policies and regulatory requirements.; Product teams compare security scores across different model providers and versions, selecting the most robust AI for their application.; DevOps engineers use the Python SDK to automate red teaming tests in staging environments, catching data leakage and unsafe behavior early in the development cycle..
- What are alternatives to ModelRed?
- See the ranked list of ModelRed alternatives in the AI Security category on ContentBuffer.
Opens in a new tab on ModelRed website.
Comments
Be the first to comment
Discover more AI tools like this
Get the best AI tools, news, and resources delivered weekly.
Join 3,571 builders reading daily.