
Compliance Paid
SOC 2 Readiness Audit
Web Application 4.3/5 Web
What is SOC 2 Readiness Audit?
AI-powered SOC 2 readiness assessment for SaaS founders. Get audit-ready 10x faster with gap analysis and remediation plan.
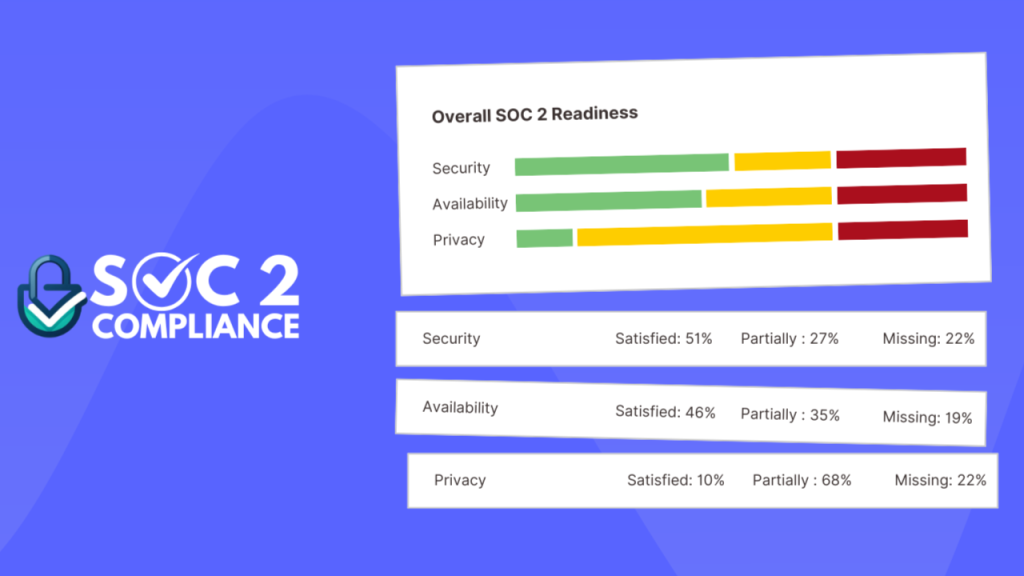
An AI-powered SOC 2 readiness assessment tool that helps SaaS founders and SMBs quickly identify compliance gaps, get a detailed gap analysis, and receive a tailored remediation plan. It offers a practice run for SOC 2 audits, reducing effort by 90% and providing results within hours instead of months. The tool includes auditor-grade questionnaires, control mapping, and an optional Ultimate Policy Package with customizable templates.
Key Features
AI-powered gap analysis
Auditor-grade questionnaire
Control mapping dashboard
Remediation plan
Policy package (Ultimate Plan)
Progress auto-save
Results within 1 business day
Human review of reports
Use Cases
SaaS founders preparing for their first SOC 2 audit use the assessment to identify missing controls and prioritize remediation, reducing audit preparation time from months to weeks.
CTOs of growing startups run the readiness check to get a clear compliance status overview, enabling them to pass vendor risk assessments and win enterprise deals.
Compliance managers at SMBs leverage the AI-driven analysis to quickly spot gaps across all five Trust Service Criteria, then implement a tailored remediation plan without hiring expensive consultants.
Founders exploring SOC 2 use the low-pressure practice run to understand auditor expectations and build a compliance roadmap, avoiding common pitfalls that lead to abandoned audits.
Engineering leads integrate the assessment results into their development workflow, ensuring security controls are embedded early and reducing rework during the actual audit.
Security officers at tech companies use the control mapping feature to track progress and demonstrate compliance readiness to stakeholders, boosting confidence before the formal audit.
SOC 2compliancereadiness assessmentgap analysisaudit preparationAI-poweredSaaSsecuritytrust services criteria
Alternatives
Frequently asked questions
- What is SOC 2 Readiness Audit used for?
- SOC 2 Readiness Audit is used for SaaS founders preparing for their first SOC 2 audit use the assessment to identify missing controls and prioritize remediation, reducing audit preparation time from months to weeks.; CTOs of growing startups run the readiness check to get a clear compliance status overview, enabling them to pass vendor risk assessments and win enterprise deals.; Compliance managers at SMBs leverage the AI-driven analysis to quickly spot gaps across all five Trust Service Criteria, then implement a tailored remediation plan without hiring expensive consultants.; Founders exploring SOC 2 use the low-pressure practice run to understand auditor expectations and build a compliance roadmap, avoiding common pitfalls that lead to abandoned audits.; Engineering leads integrate the assessment results into their development workflow, ensuring security controls are embedded early and reducing rework during the actual audit..
- What are alternatives to SOC 2 Readiness Audit?
- Alternatives to SOC 2 Readiness Audit include Vanta, Drata, Secureframe. See the full ranked list of SOC 2 Readiness Audit alternatives on ContentBuffer.
Opens in a new tab on SOC 2 Readiness Audit website.
Comments
Subscribe to join the conversation...
Be the first to comment
Discover more AI tools like this
Get the best AI tools, news, and resources delivered weekly.
Join 3,568 builders reading daily.
Also get