🛡️Replit Rebuilds Its Sandbox Engine on MicroVMs Across Hundreds of Millions of Projects
Your agent sandbox just got its own kernel
TL;DR
Replit finished rewriting its sandbox engine around microVMs, giving every sandbox its own Linux kernel. The migration covered hundreds of millions of projects with no data loss. If you run agents that touch real systems, this is the isolation model to copy.
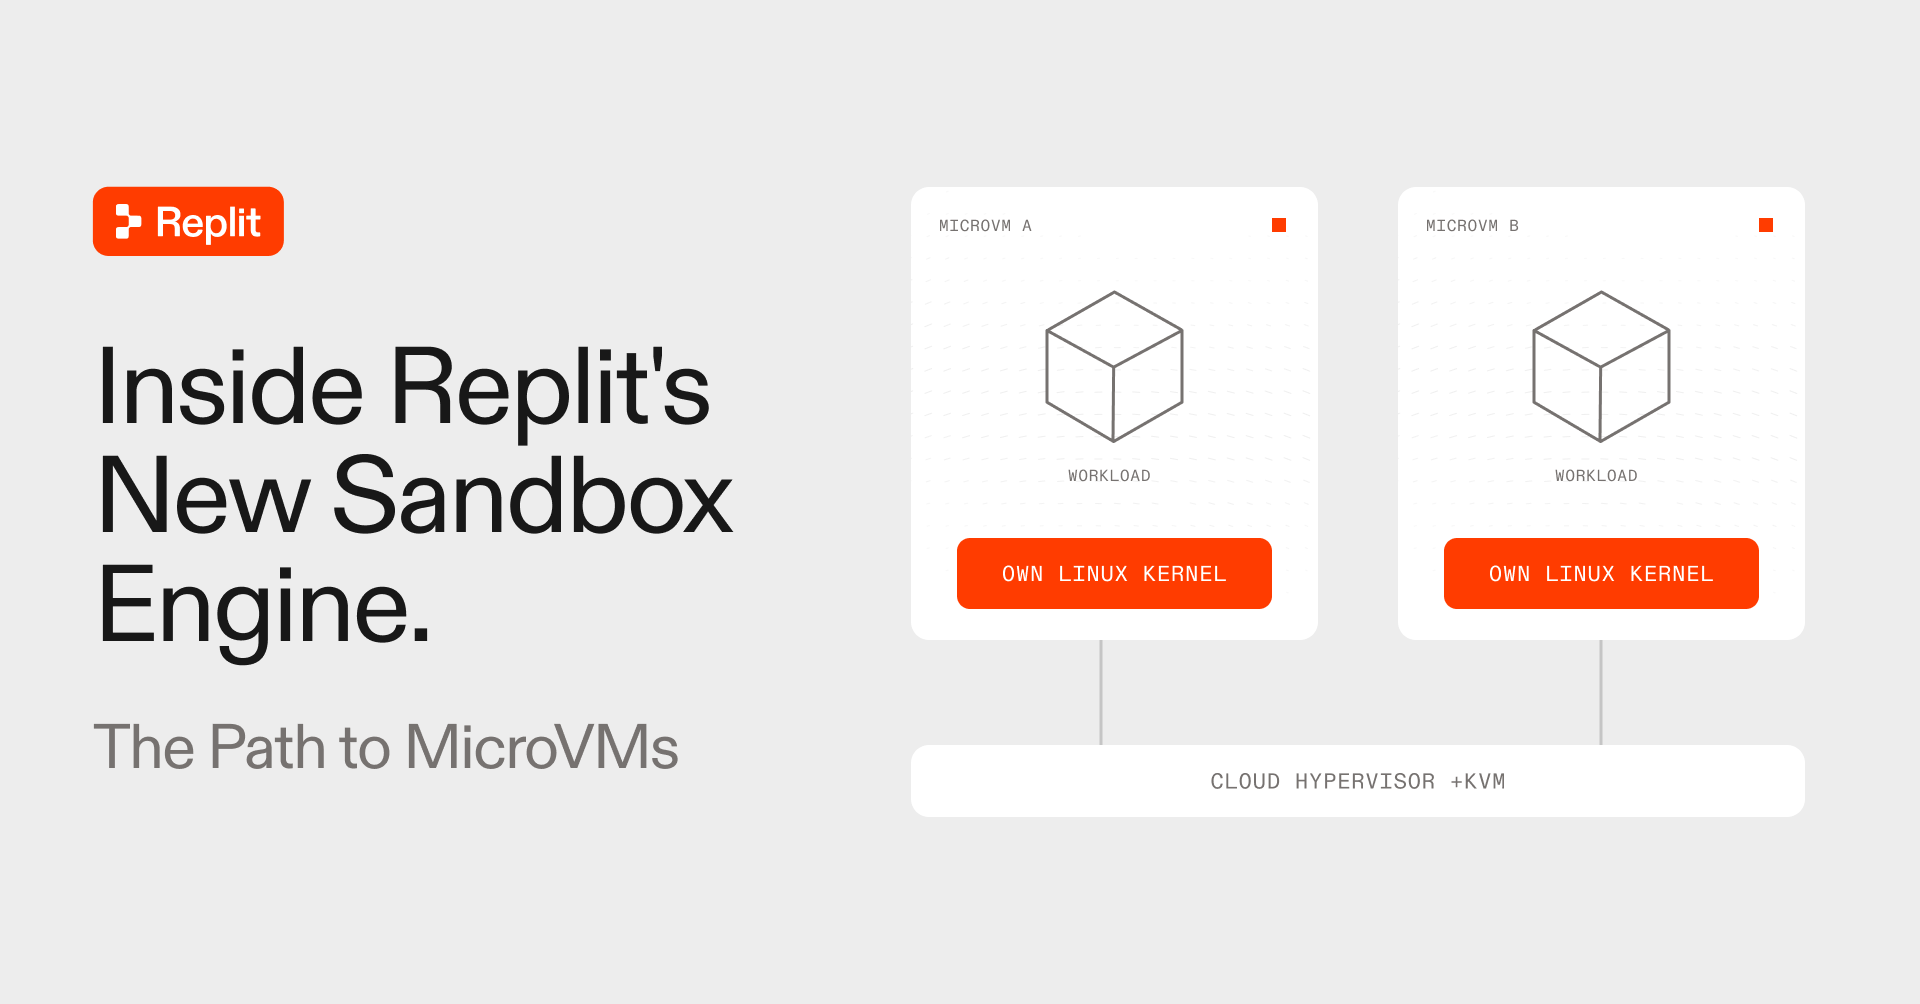
Replit just finished rewriting its sandbox engine, and the big change is simple: each sandbox now runs in its own microVM with its own Linux kernel. The old setup used containers, which share the host kernel. That's a problem when Linux kernel CVEs that allow local privilege escalation keep piling up, and AI tooling is finding them faster than ever. Why should you care? If you're building agents that run code, the isolation boundary just moved. Replit's self-driving company runs agents that investigate incidents, review code, analyze business data, and triage support tickets on this same foundation. The new engine also brings Replit into customers' AWS, Google Cloud, or Azure accounts, which matters if your security team won't let sandboxes leave your cloud. The numbers: Replit migrated hundreds of millions of projects without data loss. The engine runs on Cloud Hypervisor, shares rust-vmm components with Firecracker, and uses KVM to separate each sandbox from the host and other tenants. Work started in November 2025, and the team spent the following months hardening it before rollout.
Key Points
Each sandbox runs as a microVM with its own Linux kernel, a change from the previous container runtime that shared the host kernel across all tenants.
Keep reading — it's free
Enter your email to keep reading — plus the best of AI & tech, daily. Free, forever.
Already a member? Sign in
Comments
Be the first to comment